Zero-trust principles ensure only verified users and devices can access Torus assets. Data stays encrypted whether it’s moving or stored, which keeps operational information protected. Our systems meet the major grid and industrial security standards, including NERC CIP and IEC 62443.

Maintain defensibility as new assets connect
Every Torus system ships with cyber and physical security built in, and our team monitors each one 24/7 once it’s live. You get new capacity on the grid, and each Torus asset stays secure from the moment it connects.
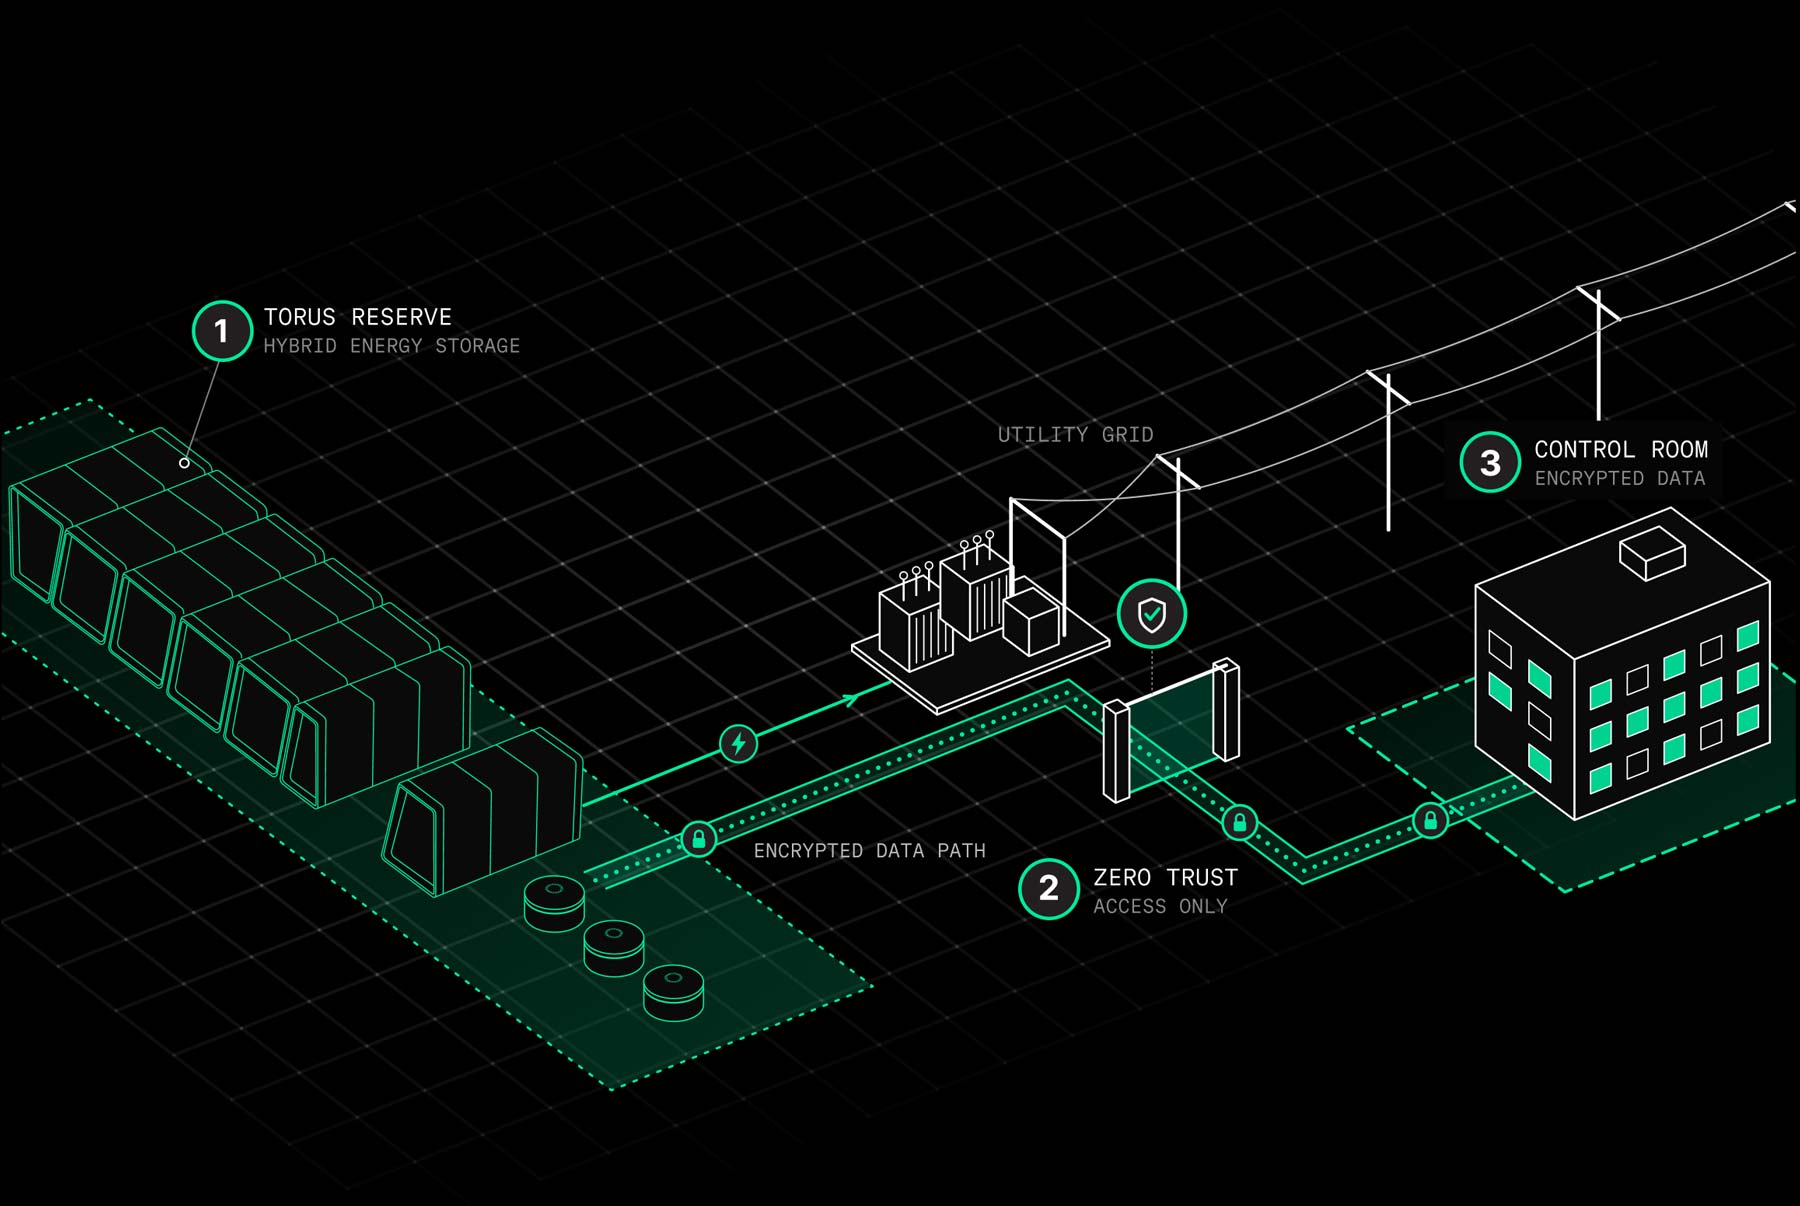
Block unauthorized access
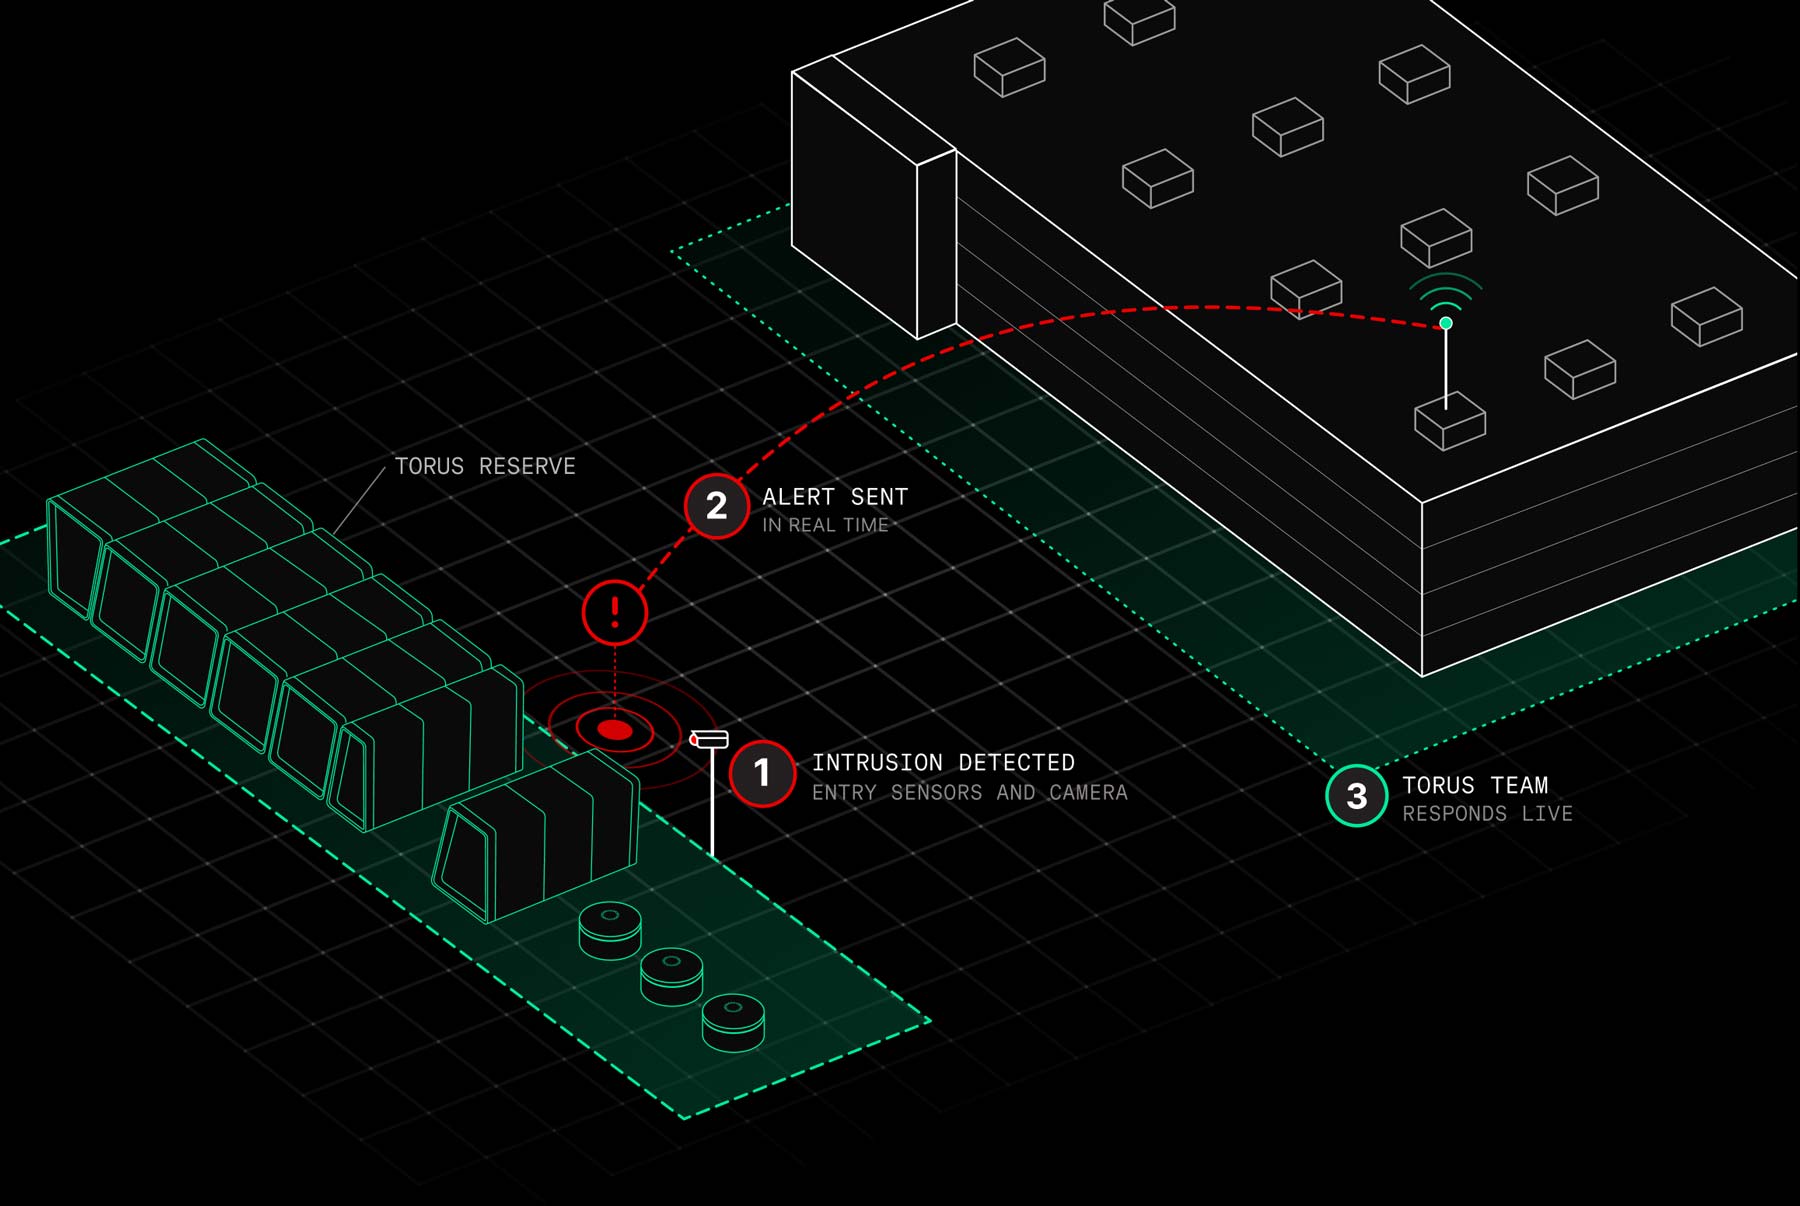
Detect threats in real time
Every Torus system includes intrusion detection. Our team monitors each asset 24/7 and analyzes millions of data points per system per day. Millisecond-level behavioral analysis flags unusual activity, like unauthorized access attempts or abnormal performance. When an alert comes in, our team investigates and responds in real time.
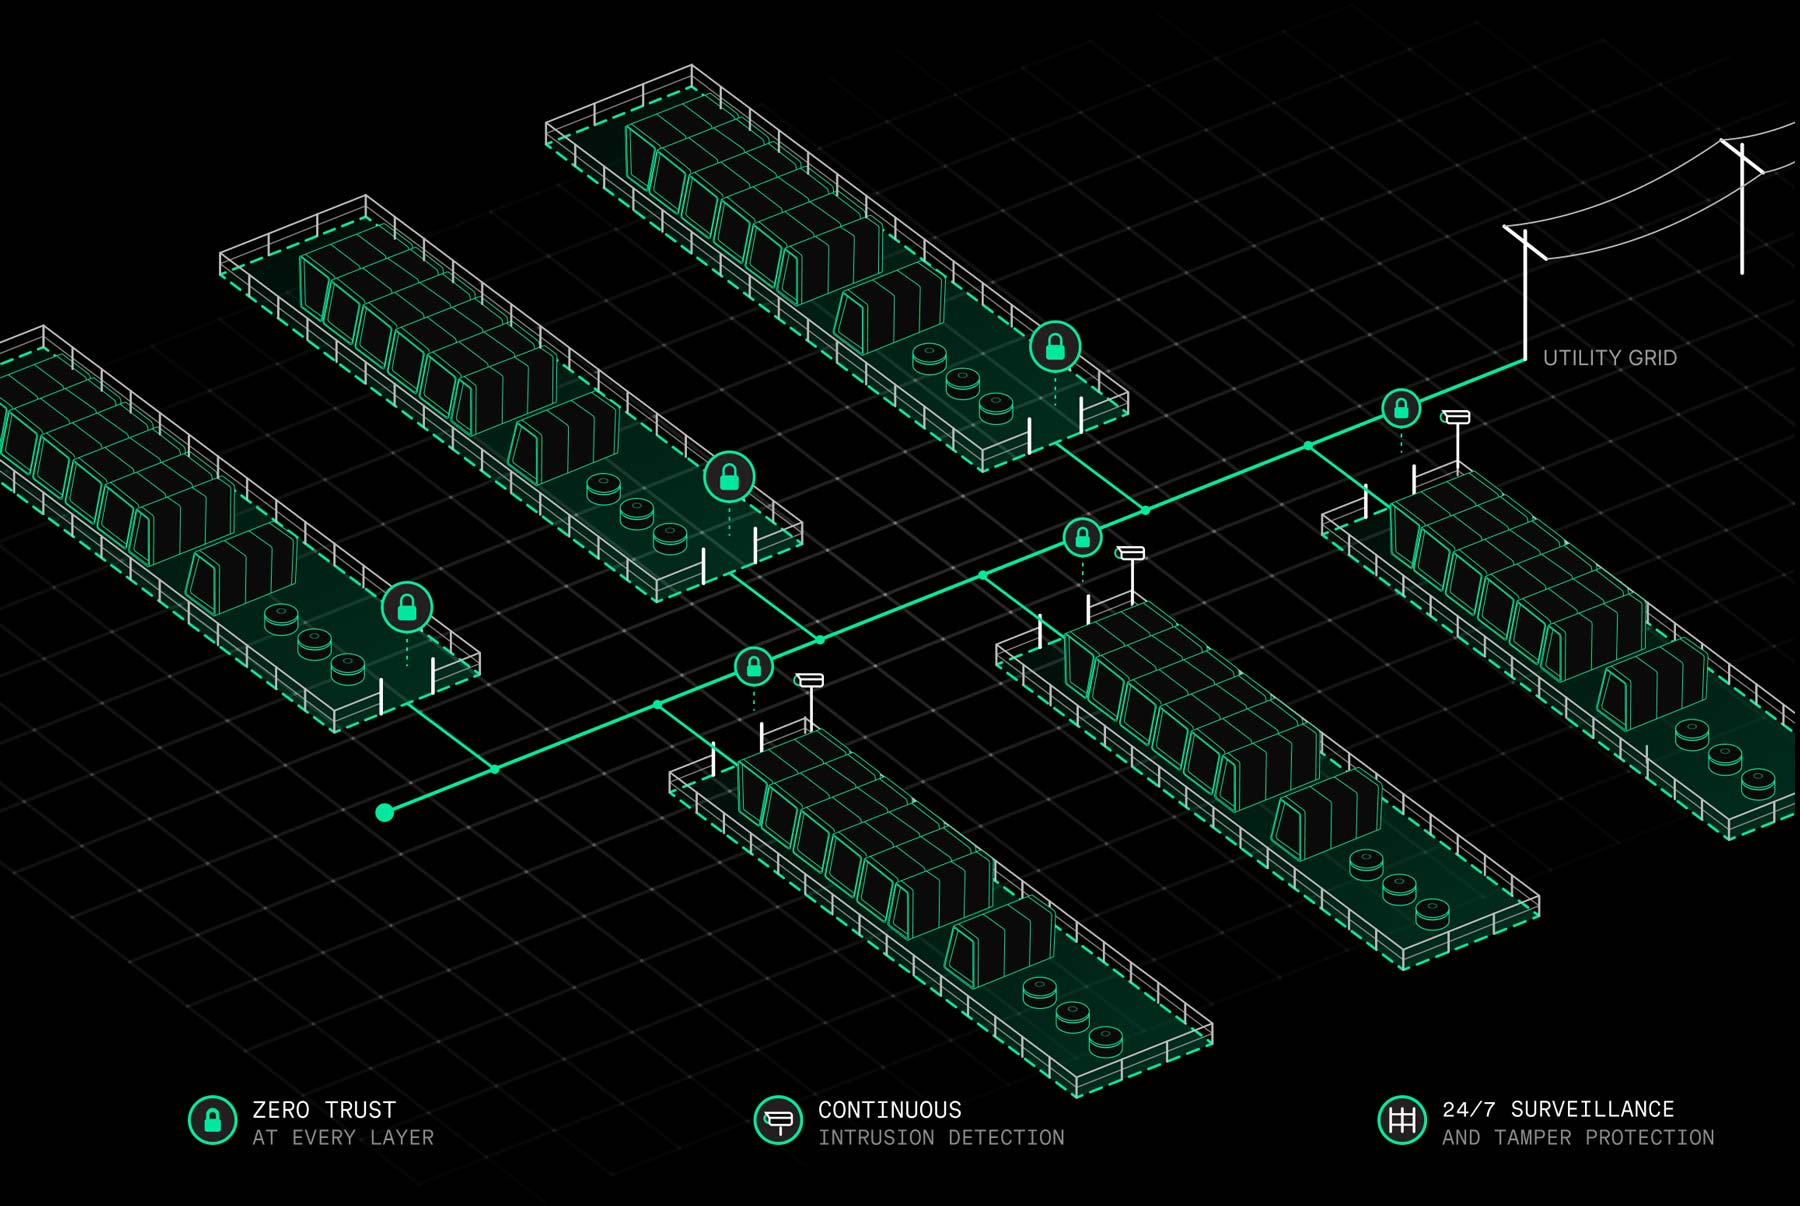
Stay secure as you scale
Each Torus system ships with the same firewall, Zero Trust access controls, encryption, and intrusion detection. Your security team reviews one standard once instead of evaluating each new site from scratch. As your fleet grows across your service territory, our team monitors every system 24/7, so security isn't compromised as you scale.
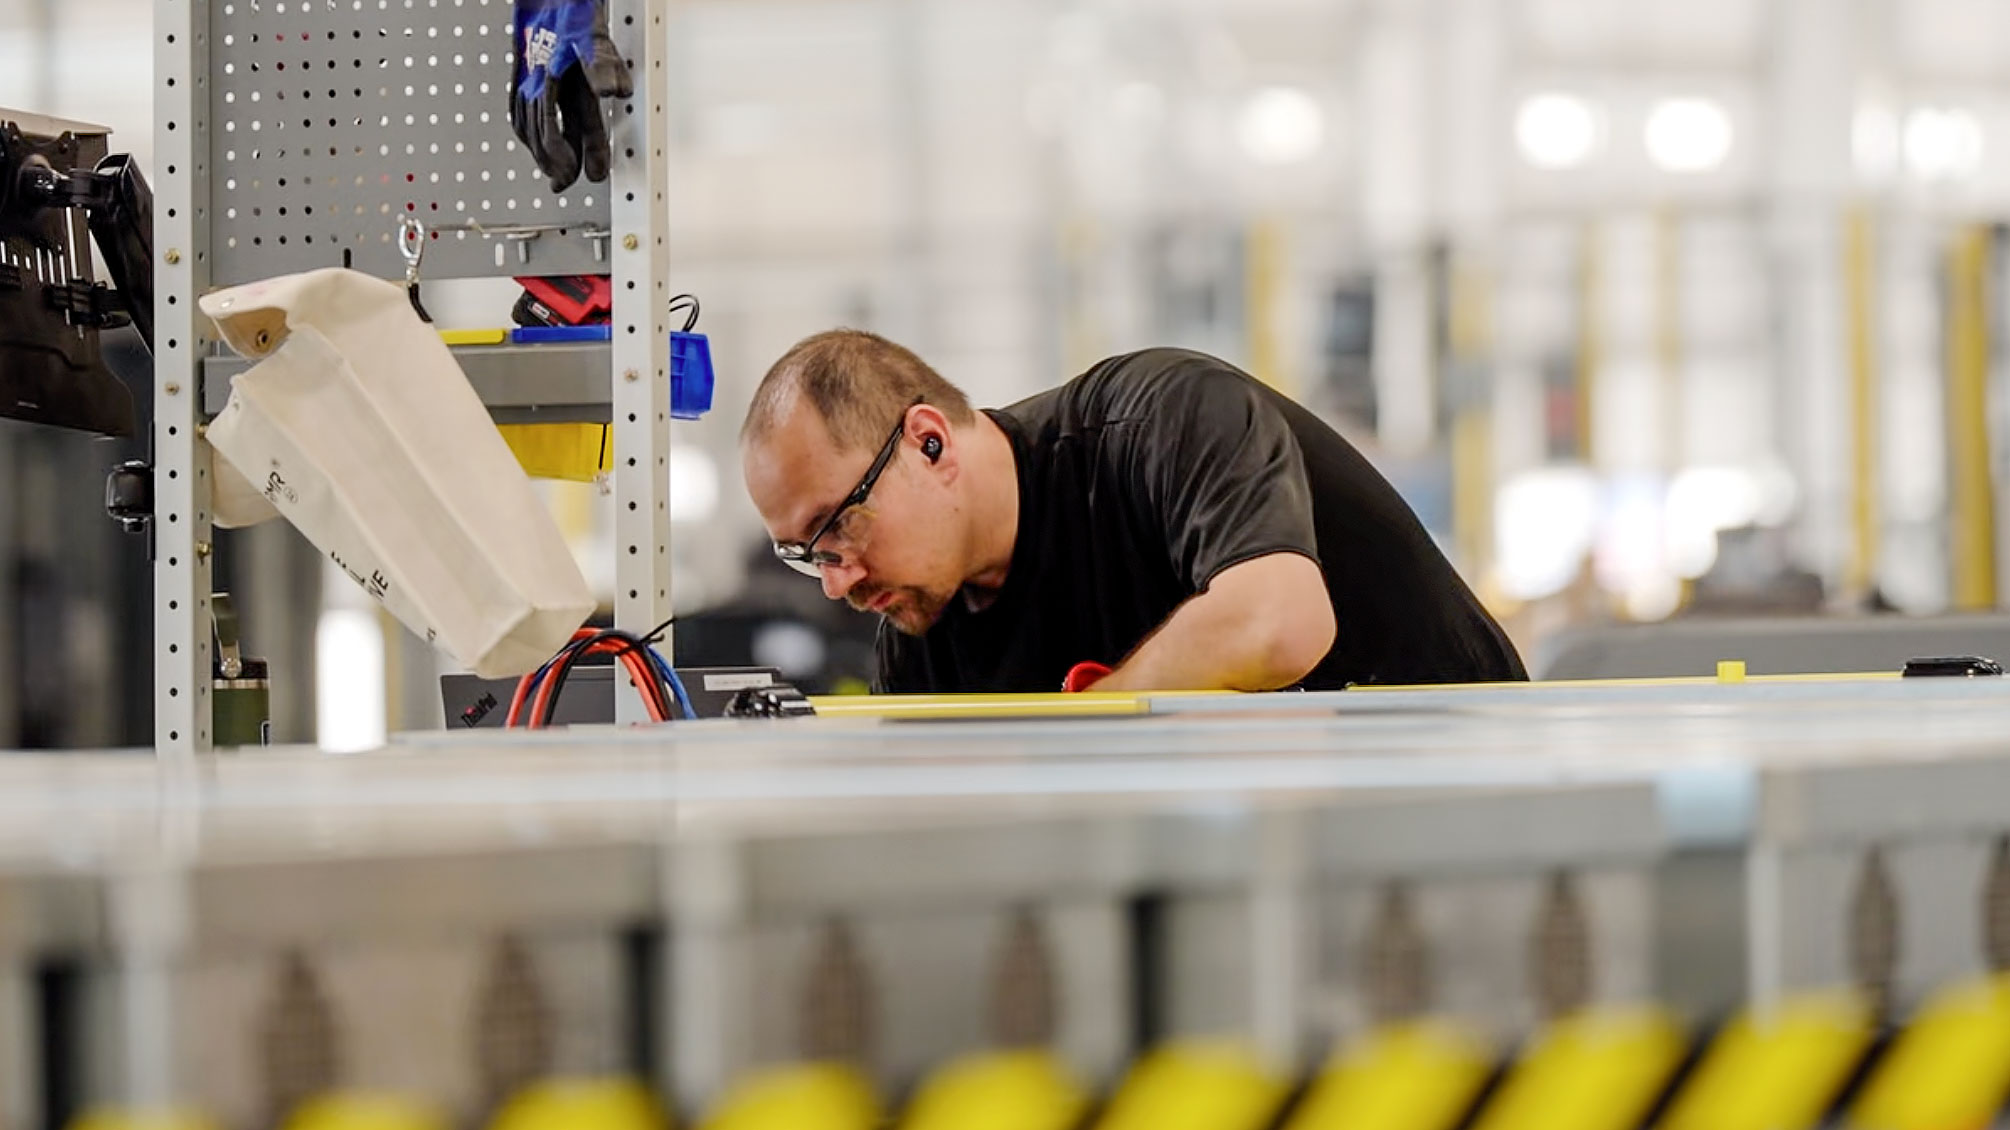
Built with U.S.-made hardware
Torus designs, engineers, and manufactures its systems across 582,000 sq. ft. of U.S. manufacturing space. We build key components in house, which minimizes unknowns in the hardware getting connected to the grid.
Built-in security
Torus Protect
Torus Protect is the cyber and physical security layer built into every Torus system. It combines a Layer 7 stateful firewall with Zero Trust access, TLS 1.3 and AES-256 encryption, and physical intrusion detection, and it meets NERC CIP, IEC 62443, and NIST 800-171 standards.